News
Chinese Find Obvious Tesla Model S Security Flaw

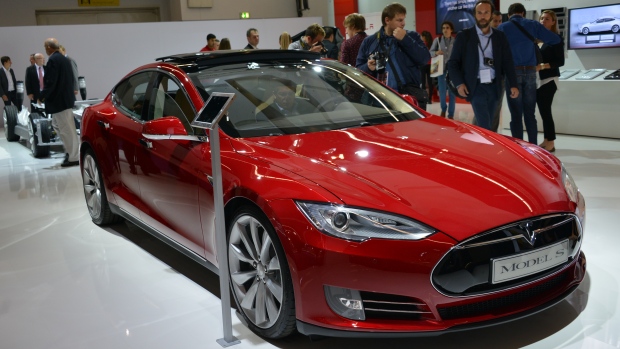
 A group of Chinese hacker reported that the Model S has a security flaw. We say, welcome to reality. Any system that is connected, whether physical or wireless, has a potential security flaw.
Model S has a security flaw
The Tesla Model S security flaw is making its round lately. It has to make you wonder when reports on security exploits related to computer systems appear. Modern computers, including cars and their wireless technologies have many open ports and channels. A long, long time ago, when I was learning about Novell servers, (yes, I’m that old) my teacher taught me that a truly un-hackable computer is one without a mouse, keyboard or Internet connection. It helped to understand that once a port is open, either with a keyboard of wireless connection, even if secured, there is still a potential vulnerability.
The Model S open connections mean potential security flaw
The Model S is not really a car. It’s more of a future template of what every car will soon look like. It is more of a rolling computer on wheels, which handles quite well. But the Tesla Model S is always connected, either to Tesla Motors, or the Internet, as well as many other types communication is happening. What this means is that the Model S is, by definition, as vulnerable as its weakest point in the security chain. So is it any wonder to hear that the Model S, the most Internet-connected and remotely-connected electric vehicle (EV) on the market today, has a major security flaw? It shouldn’t. Anything connected cars, even Tesla’s Model S means it can be hacked and has security flaws.
According to TransportEvolved, Sina Weibo announced a Chinese Internet security company called Qihoo 360, found Tesla Model S security flaw. This is one of the most common security issue with anything connected and it means a crafty hacker can remotely access and unlock your Tesla Model S, as well as sound the horns, use the headlights, wipers, and even the panoramic sunroof. Are you scared yet? At the very least, if it rains, you might get annoyed.
Making sense of the Tesla Model S security flaw
Once we take a few steps back, we can see a pattern emerging from this Tesla Model S security flaw news. First, it was announced a day before one of the biggest security conference in China, the 2014 SyScan +360. Add to this that the conference is awarding a $10,000 prize to whoever successfully hacks into a Tesla Model S, and you get a better picture of what is happening. The Tesla Motors Model S is as secured as can be, and will continue to be more secured as each individual security flaws are discovered.
Tesla Motors was quick to reassure us with the following: “While Tesla is not associated with the conference and is not a sponsor of the competition, we support the idea of providing an environment in which responsible security researchers can help identify potential vulnerabilities. We hope that the security researchers will act responsibly and in good faith.” Whether open or closed sources, nothing is 100% secured if it is connected.
But joking apart, news of the Tesla Model S security flaw is a welcome relief in a world of over-confidence and side-blinders. In the meantime, as user and hacker feedback rolls in, Tesla will rewrite some APIs and take a closer look at some of the certificates it uses. So far, if sounding your horn, opening your doors and sunroof are the biggest threats, we can say that the latest Tesla Motors Model S security flaw is only a potential… so far.

Lifestyle
Tesla’s mirrorless Cybercab will give riders a visibility upgrade
Tesla engineer confirms Cybercab update letting riders pull up rear and repeater cameras on demand.

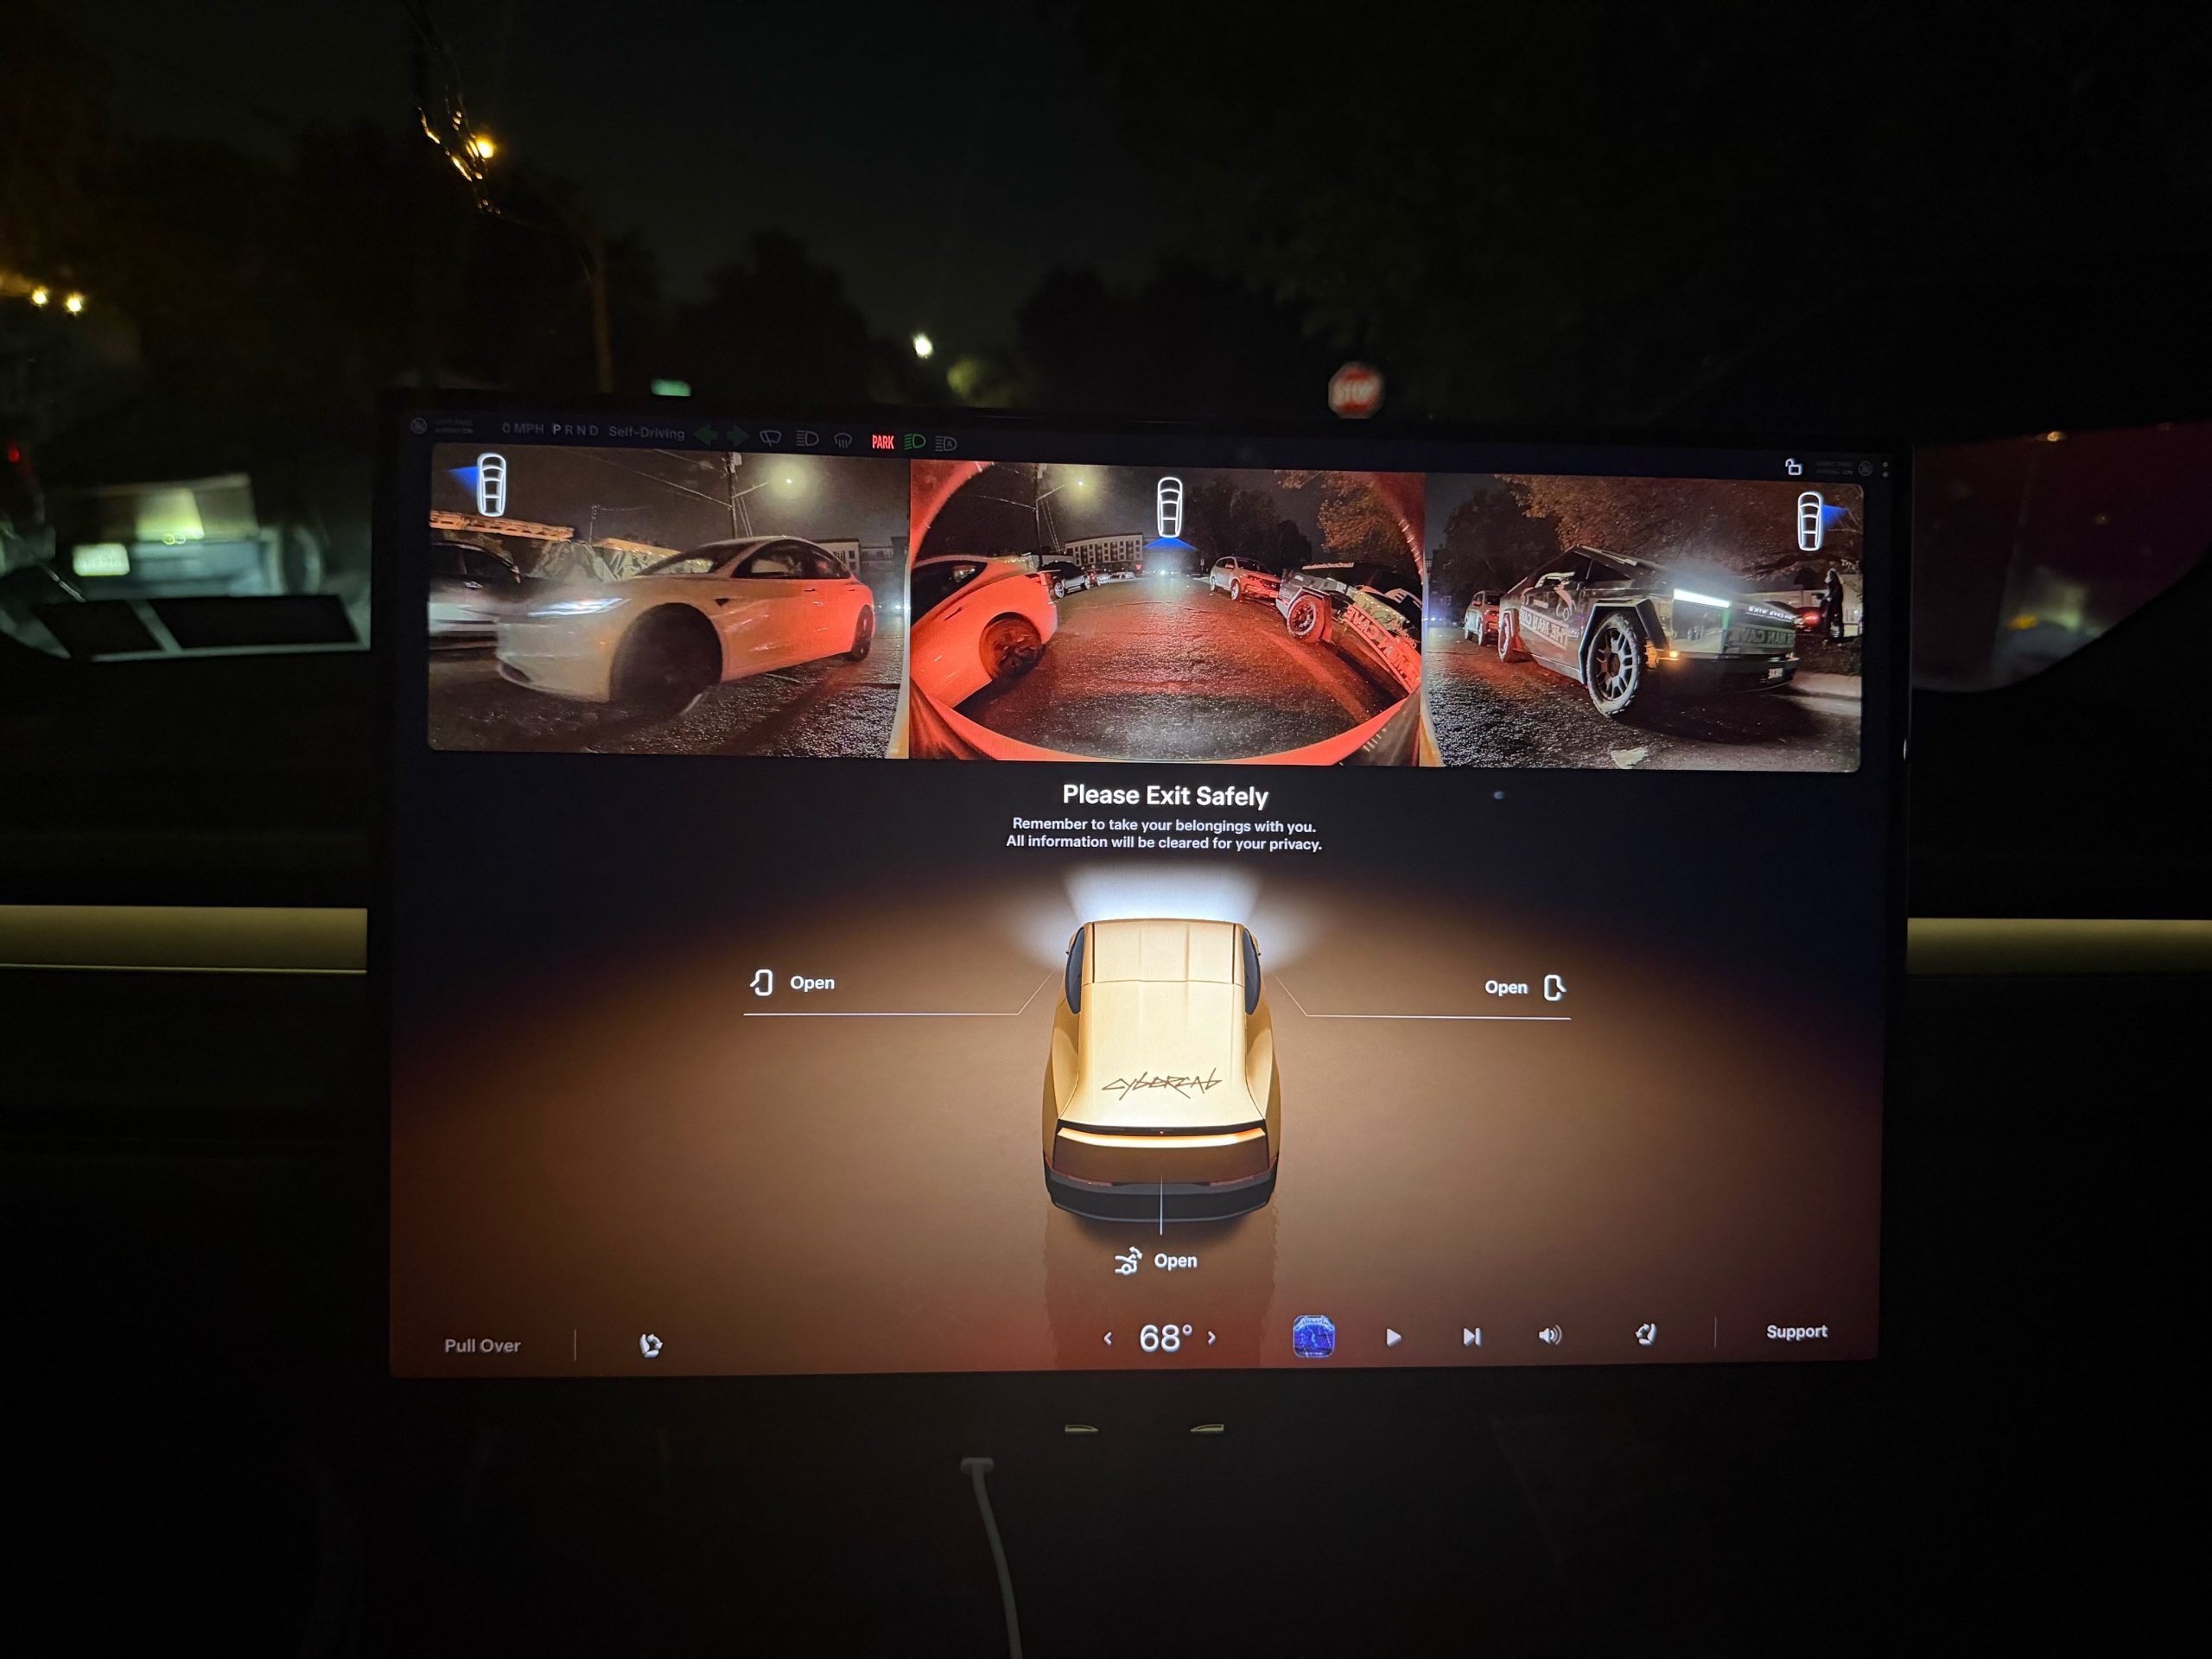
Tesla is working on a Cybercab update that would let passengers pull up the vehicle’s rear and side cameras on demand, and the request came straight from a rider.
The exchange played out on X late Friday. Cybercab rider Dan Burkland shared photos of the two-seater’s cabin screen after an evening ride, praised the UI team’s work, and left one request: let riders open the rear and repeater cameras whenever they want, “especially for peace of mind.” Tesla UI software engineer Evan (@CarCoder) answered with two words: “In development.”
The Tesla UI team absolutely crushed it with the infotainment software. Nicely done @CarCoder!
One feature request: Allow folks to pull up the rear & repeater cameras on demand. This would be great especially for peace of mind. https://t.co/mNAOSLx6pE
— Dan Burkland (@DBurkland) October 10, 2026
The idea fits a pattern Teslarati has tracked since public rides began. Days after paid Cybercab service opened in Austin, Tesla sent riders a survey that asked them to rate the touchscreen, the app and the cabin, and to pick the features they wanted most. We reported on that survey in September, and a camera view is the kind of small software change Tesla can push quickly if riders keep asking.
It also speaks to something unique about the vehicle. With no steering wheel, no pedals and no driver, passengers have no mirror to check and no way to see behind them. The hardware is clearly built for camera awareness, from the repeater cameras to the rear camera. Letting a passenger look through those same cameras would give a nervous first time rider a way to confirm what is around the car.
The timing matters because the fleet is growing fast. Tesla’s Robotaxi account said on Saturday that more than 300 Cybercabs are now serving Austin, an eightfold increase in 30 days, and Tesla AI chief Ashok Elluswamy named Dallas as the next city. More cars and more cities mean more people riding in a driverless vehicle for the first time, which is exactly when small trust features carry weight.
For now, the feature is confirmed only as in development. If Tesla follows its usual pattern with Cybercab software, riders could see it appear in a point release without any announcement, and Teslarati will watch for it.
News
Tesla’s Cybercab fleet jumped 8x in a month, with Dallas up next
Tesla confirms its first official Cybercab fleet number as Austin scales fast and Dallas looms.
Tesla says more than 300 Cybercabs are now serving Austin, the first time the company has put an official number on its active Cybercab fleet. The figure came from the Robotaxi account on X on Saturday, which wrote that one month after launch the service had “scaled to 300+ Cybercabs serving Austin – an 8x increase in 30 days.”
Ashok Elluswamy, Tesla’s head of AI software, quoted the post with a line that carried the bigger news. “Two years since the 10/10 Cybercab WeRobot event, the cabs are everywhere in Austin now. Dallas soon,” he wrote. It is the first time Tesla has named the next city for public Cybercab rides.
One month after launch, we’ve scaled to 300+ Cybercabs serving Austin – an 8x increase in 30 days https://t.co/EagJy2JAsm
— Robotaxi (@robotaxi) October 10, 2026
Tesla opened Cybercab rides to the public in Austin on September 4, as Teslarati reported, a day after an invite only launch event. The ramp since then has been steep. Our September 28 report had the fleet at well over 100 units after availability jumped from 58 to 125 in a single week. On Thursday, Tesla added 150 Cybercabs to the Texas automated vehicle registry, lifting its registered count to 319 from 169. The first seven appeared on the registry on August 31.
RobotaxiTracker, a community site that counts vehicles from sightings and state records, listed 275 vehicles in unsupervised service in Austin on Saturday, 105 of them Cybercabs, which is well below Tesla’s figure. Tracker counts can lag official numbers, though Sawyer Merritt noted that Cybercab wait times in Austin stayed short on Saturday evening even with more than 2,000 fans in town for X Takeover.
Regulators are watching the rollout. NHTSA opened an audit query into Tesla’s certification that the Cybercab meets federal safety standards, and sworn answers are due October 30. Tesla reports third quarter earnings on October 21, which gives the company a natural venue to define its fleet numbers and put a date on Dallas.
Elon Musk
Elon Musk roasts India’s billionaire Mukesh Ambani as Starlink fight heats up
Elon Musk sarcastically calls Mukesh Ambani ‘Prime Minister’ as the Starlink India standoff escalates again.
Elon Musk escalated his public fight over Starlink’s launch in India on Friday, addressing Reliance chairman Mukesh Ambani as “Prime Minister Ambani” in a sarcastic post on X. “Please accept my humble apologies for not realizing that you are the real boss of India,” Musk wrote, before accusing Ambani of “monopolistic exploitation” and asking whether he would “consider allowing Starlink to compete.” In follow up posts, he said Starlink has proven essential during natural disasters and would help parts of India with no internet access.
The post came two days into a fight that Musk sparked up on Wednesday, when he said Starlink was “being blocked by certain oligarchs in order to maintain their monopolistic chokehold on the Indian people.” He called it “a crime against the people of India” and left the names out, adding only, “You can guess who they are.” Jio and Airtel together hold more than 80% of India’s telecom market. On Thursday, Musk asked whether Ambani is “the real boss of India” and said Starlink has spent five years complying with “every single law and requirement” of the Indian government.
Dear Prime Minister Ambani,
Please accept my humble apologies for not realizing that you are the real boss of India.
Naturally, you would prefer to maintain your monopolistic exploitation of the great people of India, but would you nonetheless consider allowing Starlink to compete?
There are many areas of India, as there are in all countries, with no Internet access, which denies children the opportunity for education and for small businesses the opportunity to sell their goods to a global market. Starlink would change their lives for the better.
Thank you 🙏
— Elon Musk (@elonmusk) October 9, 2026
India’s government has pushed back each time. The Ministry of Communications called the suggestion that its framework is unfair or discriminatory “baseless and misconceived.” Communications Minister Jyotiraditya Scindia said Friday that three companies hold satcom licenses: Starlink, Jio Satellite Communications, and Bharti backed Eutelsat OneWeb. Amazon’s Kuiper, now Amazon Leo, is still going through the process. None can launch until regulators finalize satellite spectrum pricing and the Home Ministry signs off on each company’s security compliance. Scindia said the telecom regulator and the Department of Telecommunications are close to a decision on pricing, The Hindu reported. Bharti chairman Sunil Mittal also said OneWeb is still waiting on approvals.
Starlink received its operator license in 2025 after a three year wait, and the space regulator IN-SPACe granted what industry executives called the last approval needed in July. The holdup since then centers on security, particularly concern that foreign operators could bypass Indian gateways.
Musk and Ambani have been on opposite sides of this before. In late 2024, Ambani argued for auctioning satellite spectrum, which Musk criticized as out of step with the rest of the world, and India chose administrative allocation instead. By March 2025, the two sides had signed a deal to sell Starlink devices in Reliance stores, and Starlink secured its telecom license that June. That partner is now also a competitor. Jio is reportedly weighing a constellation of 1,600 to 1,650 satellites costing an estimated $10 billion to $15 billion, while Akash Ambani has told shareholders Jio plans to lease capacity from global providers to move quickly.

Tesla’s mirrorless Cybercab will give riders a visibility upgrade

Tesla’s Cybercab fleet jumped 8x in a month, with Dallas up next

Elon Musk roasts India’s billionaire Mukesh Ambani as Starlink fight heats up

The Pentagon taps Elon Musk to design the battlefield of the future

Tesla Roadster’s new patent preps white-knuckle speeds, keeping it grounded


