News
Tesla targeted in cybersecurity attack, 222 cameras infiltrated by group of hackers

Tesla was one of several companies targeted as hackers say they obtained livestreams to 222 cameras located at factories and warehouses owned by the electric car company.
A security startup known as Verkada was hacked into by a group of hackers who gained access to over 150,000 total internet-connected security camera streams. Other companies, like Equinox and Cloudflare, were also affected by the security mishap, which gave the hackers an inside look at some company facilities. The hack also exposed an incident at a Florida hospital, where eight hospital workers were pinning a man to a bed.
Tesla had a total of 222 of its cameras across company facilities be affected in the breach.
In Tesla’s case, the company said (via Bloomberg):
“Based on our current understanding, the cameras being hacked are only installed in one of our suppliers, and the product is not being used by our Shanghai factory or any of our Tesla stores or services centers. Our data collected from Shanghai factories and other places mentioned are stored on local servers.”
The breach was performed by a group of international hackers who “intended to show the pervasiveness of video surveillance and the ease with which systems could be broken into,” Tillie Kottmann, a hacker for the group, said. Kottmann didn’t identify whether it was their real name and chose to be identified with they/them pronouns.
Kottman also said that some reasons for the hacking include:
“…Lots of curiosity, fighting for freedom of information and against intellectual property, a huge dose of anti-capitalism, a hint of anarchism — and it’s also just too much fun not to do it.”
As a result, Verkada spokespeople said in a statement that, “We have disabled all internal administrator accounts to prevent any unauthorized access.”
Tesla has been the target of several hacks in the past. In August 2020, a company employee was contacted by Egor Igorevich Kriuchkov, a Russian citizen accused of conspiring to breach the network of a US company and introduce malware to company networks. Kriuchkov offered a Giga Nevada employee $1 million to install the malware, which would allow hackers to occupy the Tesla information security team. The plan never worked out as the Giga Nevada employee contacted the FBI, who took down Kriuchkov on August 22, 2020.
Tesla employee foregoes $1M payment, works with FBI to thwart cybersecurity attack
It is unknown whether the latest security breach warrants any criminal charges. While Tesla was one victim of the attack, hospitals, jails, schools, and police departments were all affected by the security breach.

News
Verizon, AT&T and T-Mobile are trying to shut Starlink out before FCC vote
AT&T, Verizon and T-Mobile want 290 MHz cut from an FCC satellite plan before Thursday.

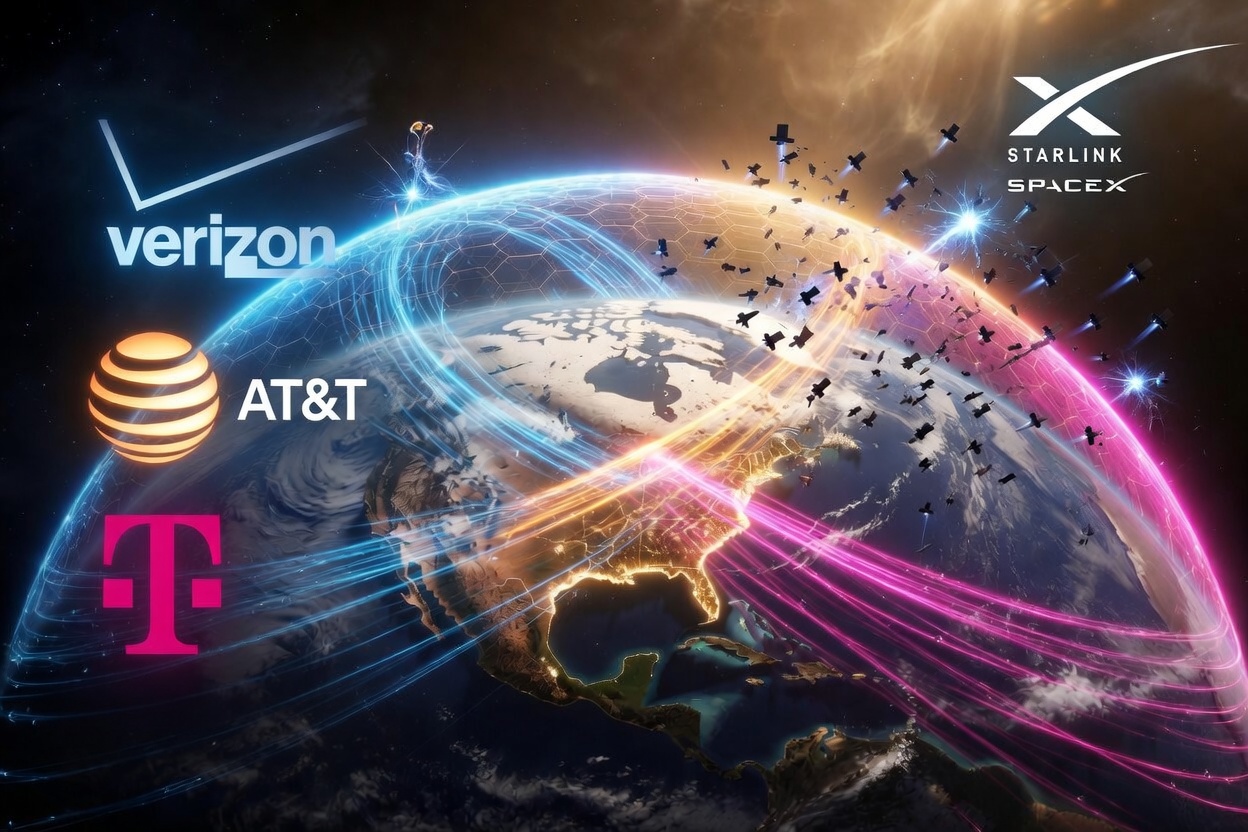
AT&T, Verizon and T-Mobile are asking the Federal Communications Commission to pull nearly 300 MHz of spectrum out of a proposal that would let satellite companies like SpaceX offer cell service directly to ordinary phones. The request lands one day before the agency votes on it.
The FCC will vote Thursday, October 29, on a notice of proposed rulemaking that would make an additional 482 MHz available for direct to device service, expanding the number of eligible bands from five to 13, according to the FCC fact sheet. It would also scrap the rule requiring a satellite operator to lease spectrum from carriers, replacing it with a certification that the operator has coexistence agreements in place or holds the terrestrial license itself.
That second path matters for SpaceX. As Teslarati reported earlier this month, SpaceX agreed to buy Grain Management’s nationwide 800 MHz portfolio to turn Starlink Mobile into a full US carrier, adding to the spectrum it already bought from EchoStar.
The carriers want two bands removed, 2.5 GHz and 3.45 GHz, which make up 290 MHz of the 482 MHz on the table. Through industry group CTIA, they argued that about 300 million users depend on those bands and that satellite operations in them are not technically feasible. T-Mobile, which calls 2.5 GHz the foundation of its Ultra Capacity 5G network, said in its own filing that satellite interference could wipe out up to 96% of a cell site’s uplink coverage area and cut uplink speeds by 88% to 99%.
Executives from all three carriers met with FCC staff on October 20, and T-Mobile CEO Srini Gopalan met separately with FCC Chairman Brendan Carr. T-Mobile’s role stands out because it is still SpaceX’s US launch partner for Starlink Mobile. The three carriers have also teamed up on their own satellite joint venture to pool spectrum, a move widely seen as a response to Starlink.
SpaceX is asking for the opposite. In an October 23 filing after meetings with FCC staff and commissioners’ offices, the company asked regulators to add the 902 to 928 MHz band to the proposal. “Doing so now saves time later,” SpaceX wrote. The company also asked the FCC to modernize interference rules and align satellite deployment requirements with those for terrestrial cell networks, saying the goal is to let satellite and ground networks work together so Americans stay connected wherever they are.
The carriers have not been shy about how they view SpaceX as a competitor. On Verizon’s third quarter earnings call Monday, its chief executive said Starlink Mobile “just can’t compete with a terrestrial network” and estimated SpaceX would need four to six years and $300 billion to $500 billion to build a full US carrier network.
Thursday’s vote will not settle which bands survive. Adopting the notice opens a public comment period, with final rules to come later in the proceeding. The FCC already considered and rejected 2.5 GHz for satellite coverage once, in 2024. SpaceX also is not the only satellite player watching: the FCC approved Amazon’s $11.6 billion acquisition of Globalstar on October 27, giving its planned direct to device fleet its own mobile satellite spectrum.
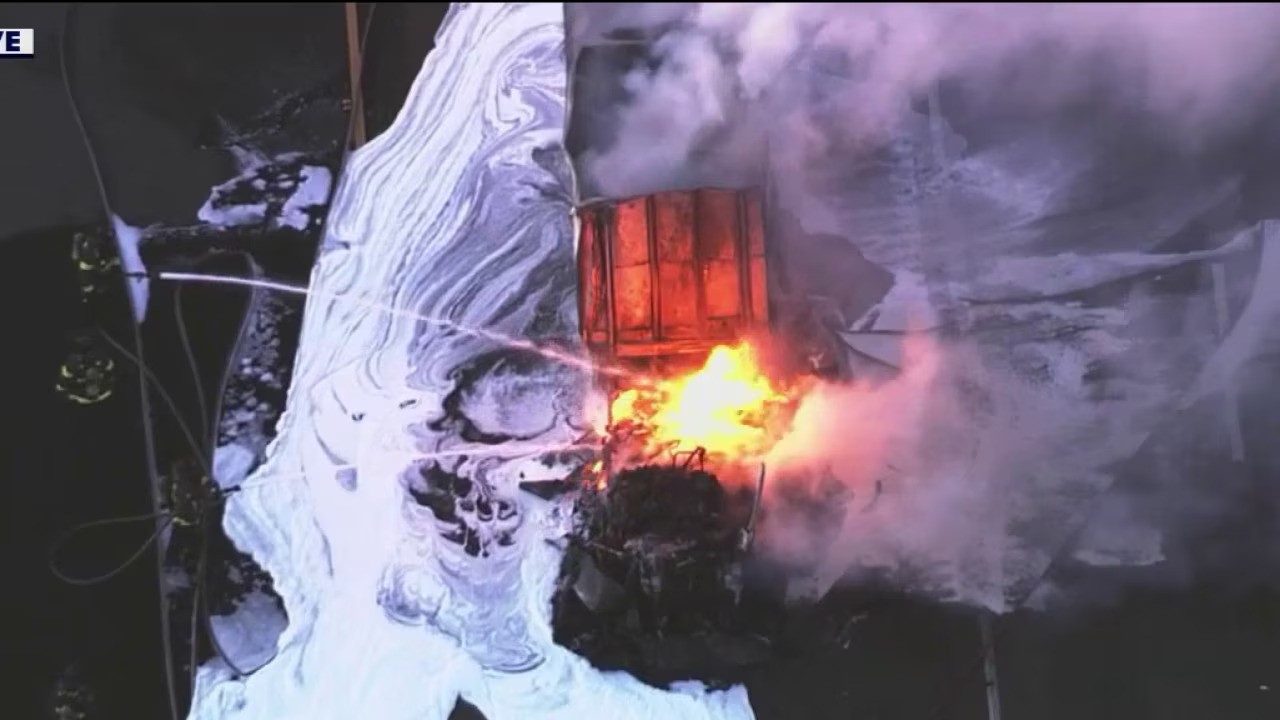
A Tesla Semi caught fire in Hayward, California, which caused both directions of traffic to shut down for hours before being completely reopened early on Wednesday, the California Highway Patrol said.
The fire occurred just after 5:30 local time in Hayward on Tuesday, as the Semi caught fire in the southbound lanes of I-880 before CHP officials made the decision to shut down both lanes of traffic due to potential risks from hazardous chemical smoke.
There were no injuries reported.
🚨 A Tesla Semi reportedly caught fire, with California Highway Patrol confirming. The Semi was on I-880 SB
An estimated 5,000 to 7,000 semi-truck and large commercial vehicle fires occur on U.S. roadways every year
— TESLARATI (@Teslarati) October 28, 2026
The cause of the fire is currently unknown, as neither Tesla nor the CHP have not determined a cause.
However, some images taken before the Semi was completely destroyed by the fire seem to indicate this might have been an older unit, as it appears to be one of the designs that Tesla shipped as part of its pilot program, before revising it and starting mass production just a month ago.
@Tslachan From on of the videos looks like it’s an old Semi (not the refresh version that recently started production) https://t.co/KzwmR2kXow
— Area Under The Curve 🎗️ (@AreaUnderCurve) October 28, 2026
At the time of publication, CHP had not returned our request for a comment for additional details, including the Semi involved and any potential collaboration on an investigation between the CHP and Tesla. We will update this story when we hear back from them.
The southbound lanes were reopened at 3:30 a.m. on Wednesday, with the northbound lanes opening last night a few hours after the fire began. The CHP did state that the lithium batteries were “incredibly difficult to extinguish,” according to NBC Bay Area.
The truck’s driver said that the Semi caught fire, but he did not have an explanation.
An estimated 5,000 to 7,000 semi-truck and large commercial vehicle fires occur on U.S. roadways every year.
Tesla’s launch of the “Emergency Drive Away” function a few months back offered owners a safe option to evacuate an area if they were in reasonable danger. The function finally got its first use in the real world, but it appears it was by mistake.
A video shared by u/Joshalander in the r/TeslaLounge subreddit recorded the instance from his vehicle and said the incident took place in Austin this past weekend during the city’s F1 Race.
“Was charging around 6 AM this past Sunday in Austin before heading to the F1 race and heard a pop. Looked over and saw the new emergency drive-away feature in action. Genuinely felt bad for the dude when he got out and realized what happened, since he looked exhausted and only seemed to half-read the prompts.”
🚨 Here’s the first look at Tesla’s Emergency Drive Away function in action:
Apparently this driver accidentally enabled it and drove forward; you can see the Supercharger pull with the car.
Tesla said previously this would cost up to $25k if not used properly. https://t.co/B4qQRrsO6B
— TESLARATI (@Teslarati) October 28, 2026
Emergency Drive Away unlatches the Supercharger connector from the vehicle, but still causes damage to both the car and the Supercharger. Tesla has said that it will cost up to $25,000 in repairs to have everything fixed back to normal.
Additionally, the company said that if it were not used in an emergency situation, the driver of the vehicle who activated the Emergency Drive Away feature would be responsible for all repair costs.
Tesla constitutes the following situations as reasonable justifications for activating the feature:
- You face an immediate threat to your life or personal safety.
- You must leave the area immediately.
- Exiting the vehicle is unsafe.
- Unplugging the charge connector would unreasonably delay your departure or expose you to a risk to your personal safety.
After using the feature, Tesla requires the driver to schedule Service so the car can be inspected.

Verizon, AT&T and T-Mobile are trying to shut Starlink out before FCC vote

Tesla Semi catches fire in California: what we know


